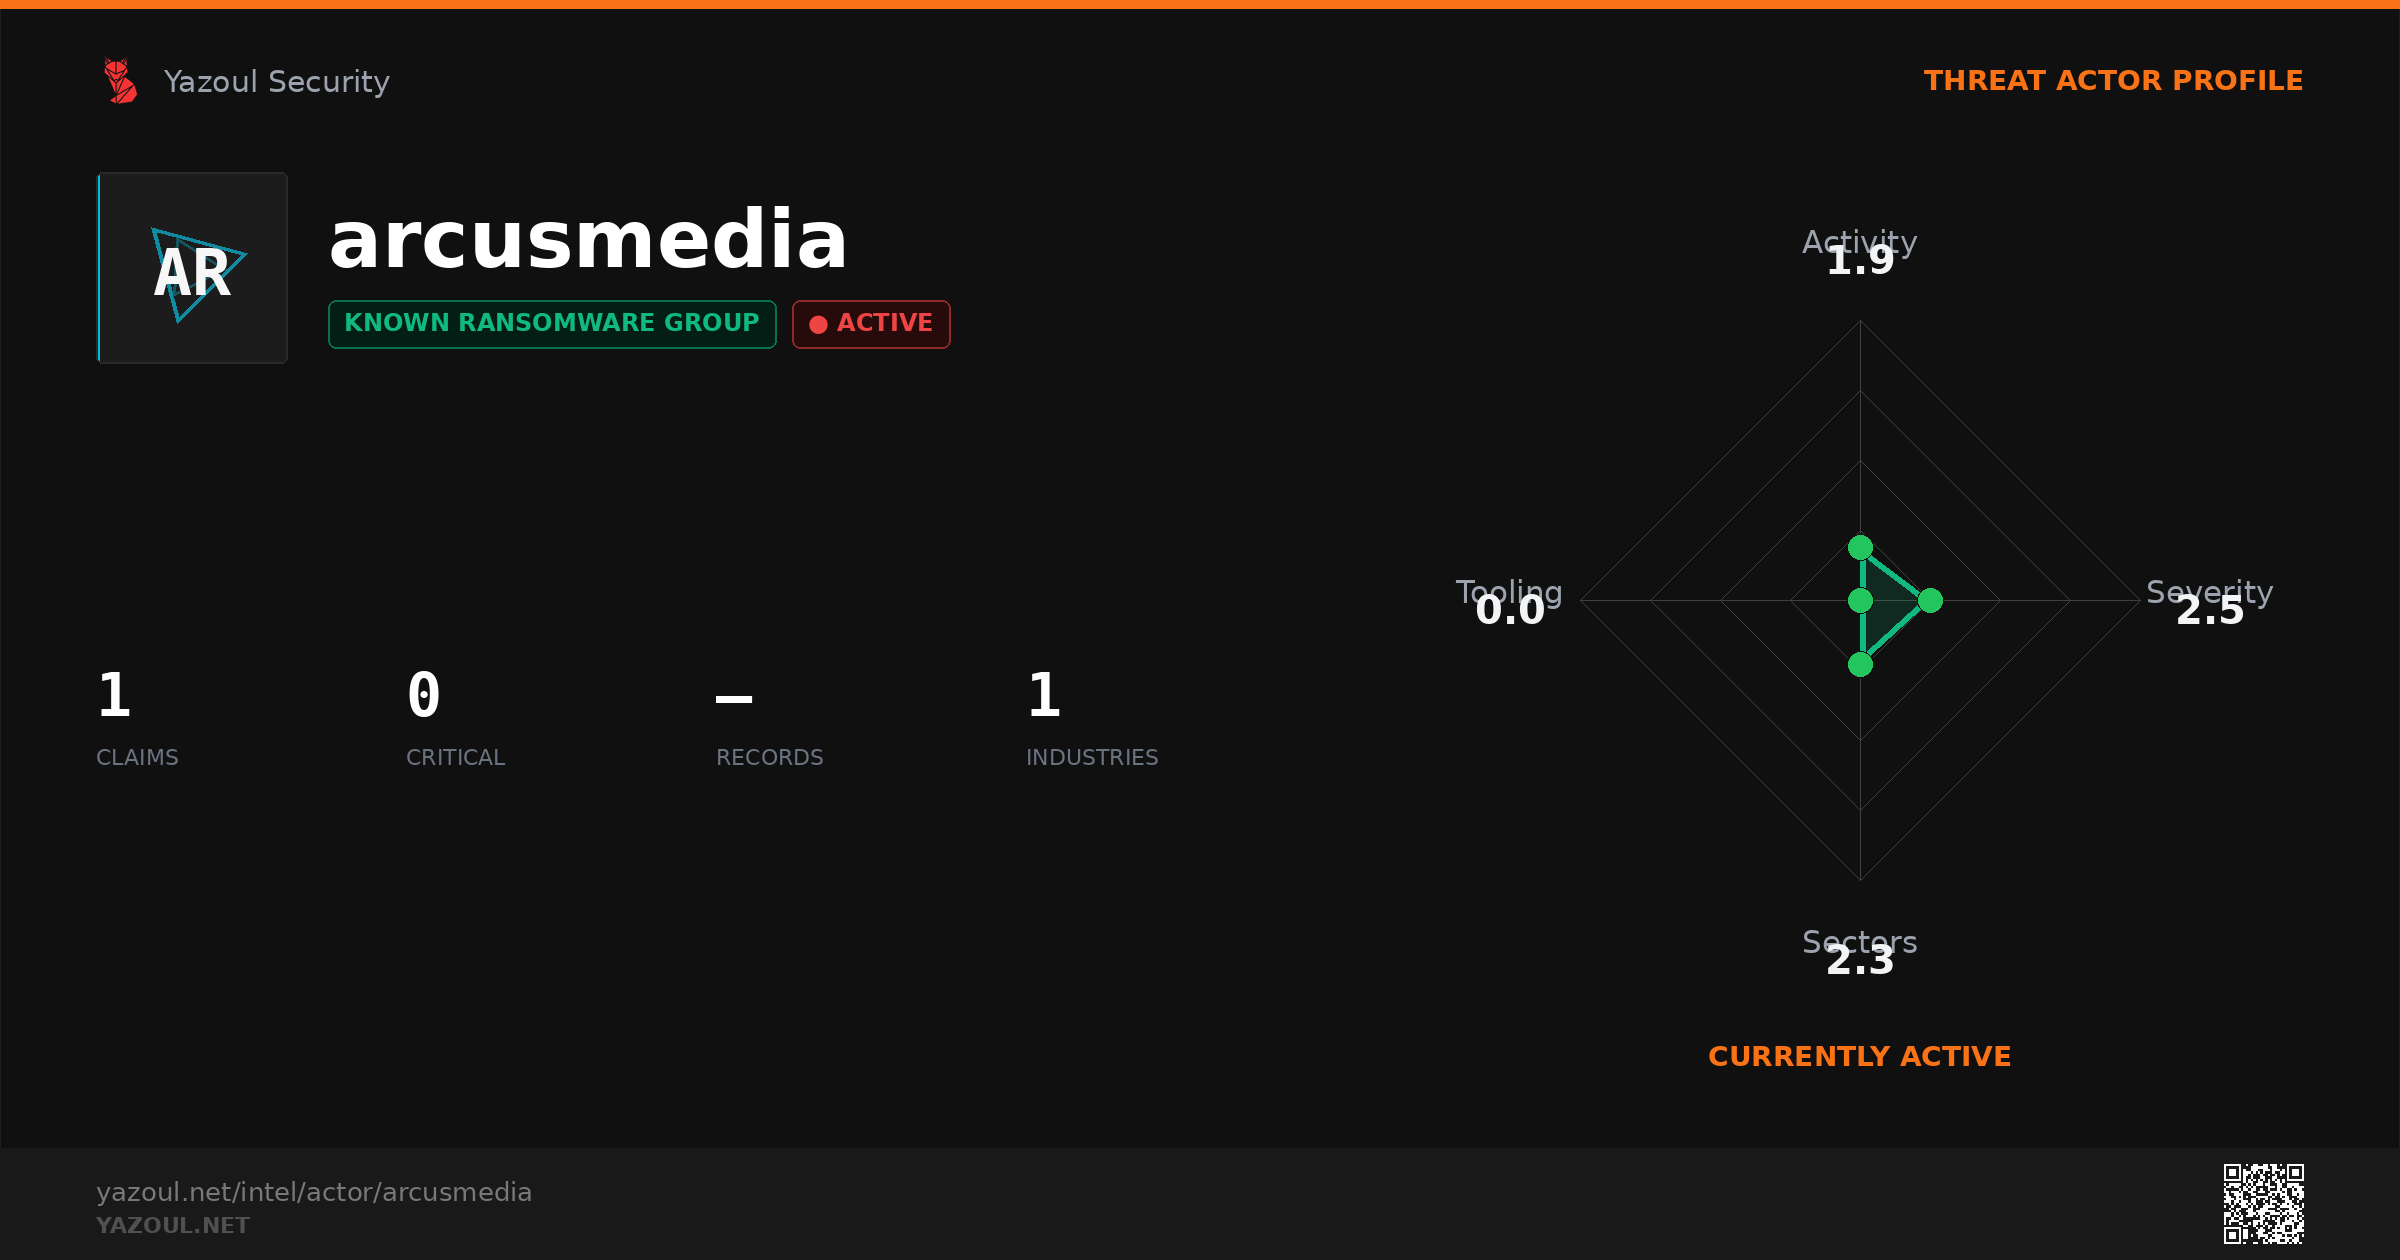
arcusmedia
Known ransomware group ACTIVE Currently active
Arcus Media is a ransomware-as-a-service group that emerged in May 2024, employing double extortion with ChaCha20 + RSA-2048 encryption and recruiting affiliates via a referral-based vetting process, claiming 50+ victims across manufacturing, healthcare, retail, and business services globally.
1
Total Claims
0
Critical
—
Records Claimed
1
Industries Hit
Active span: Sep 19, 2026 – Sep 19, 2026 · 1 organizations targeted
Currently active
Actor Threat Profile
Activity Timeline
Peak: Sep 2026 (1)Sep 2026
LessMore
Sep 2026Share this profile
Top Targeted Industries
Technology 1
Tradecraft & Infrastructure
0
Documented tools
0 / 0
MITRE tactics / techniques
1
Known leak sites