play
Known ransomware group ACTIVEAlso known as: PlayCrypt
Currently active
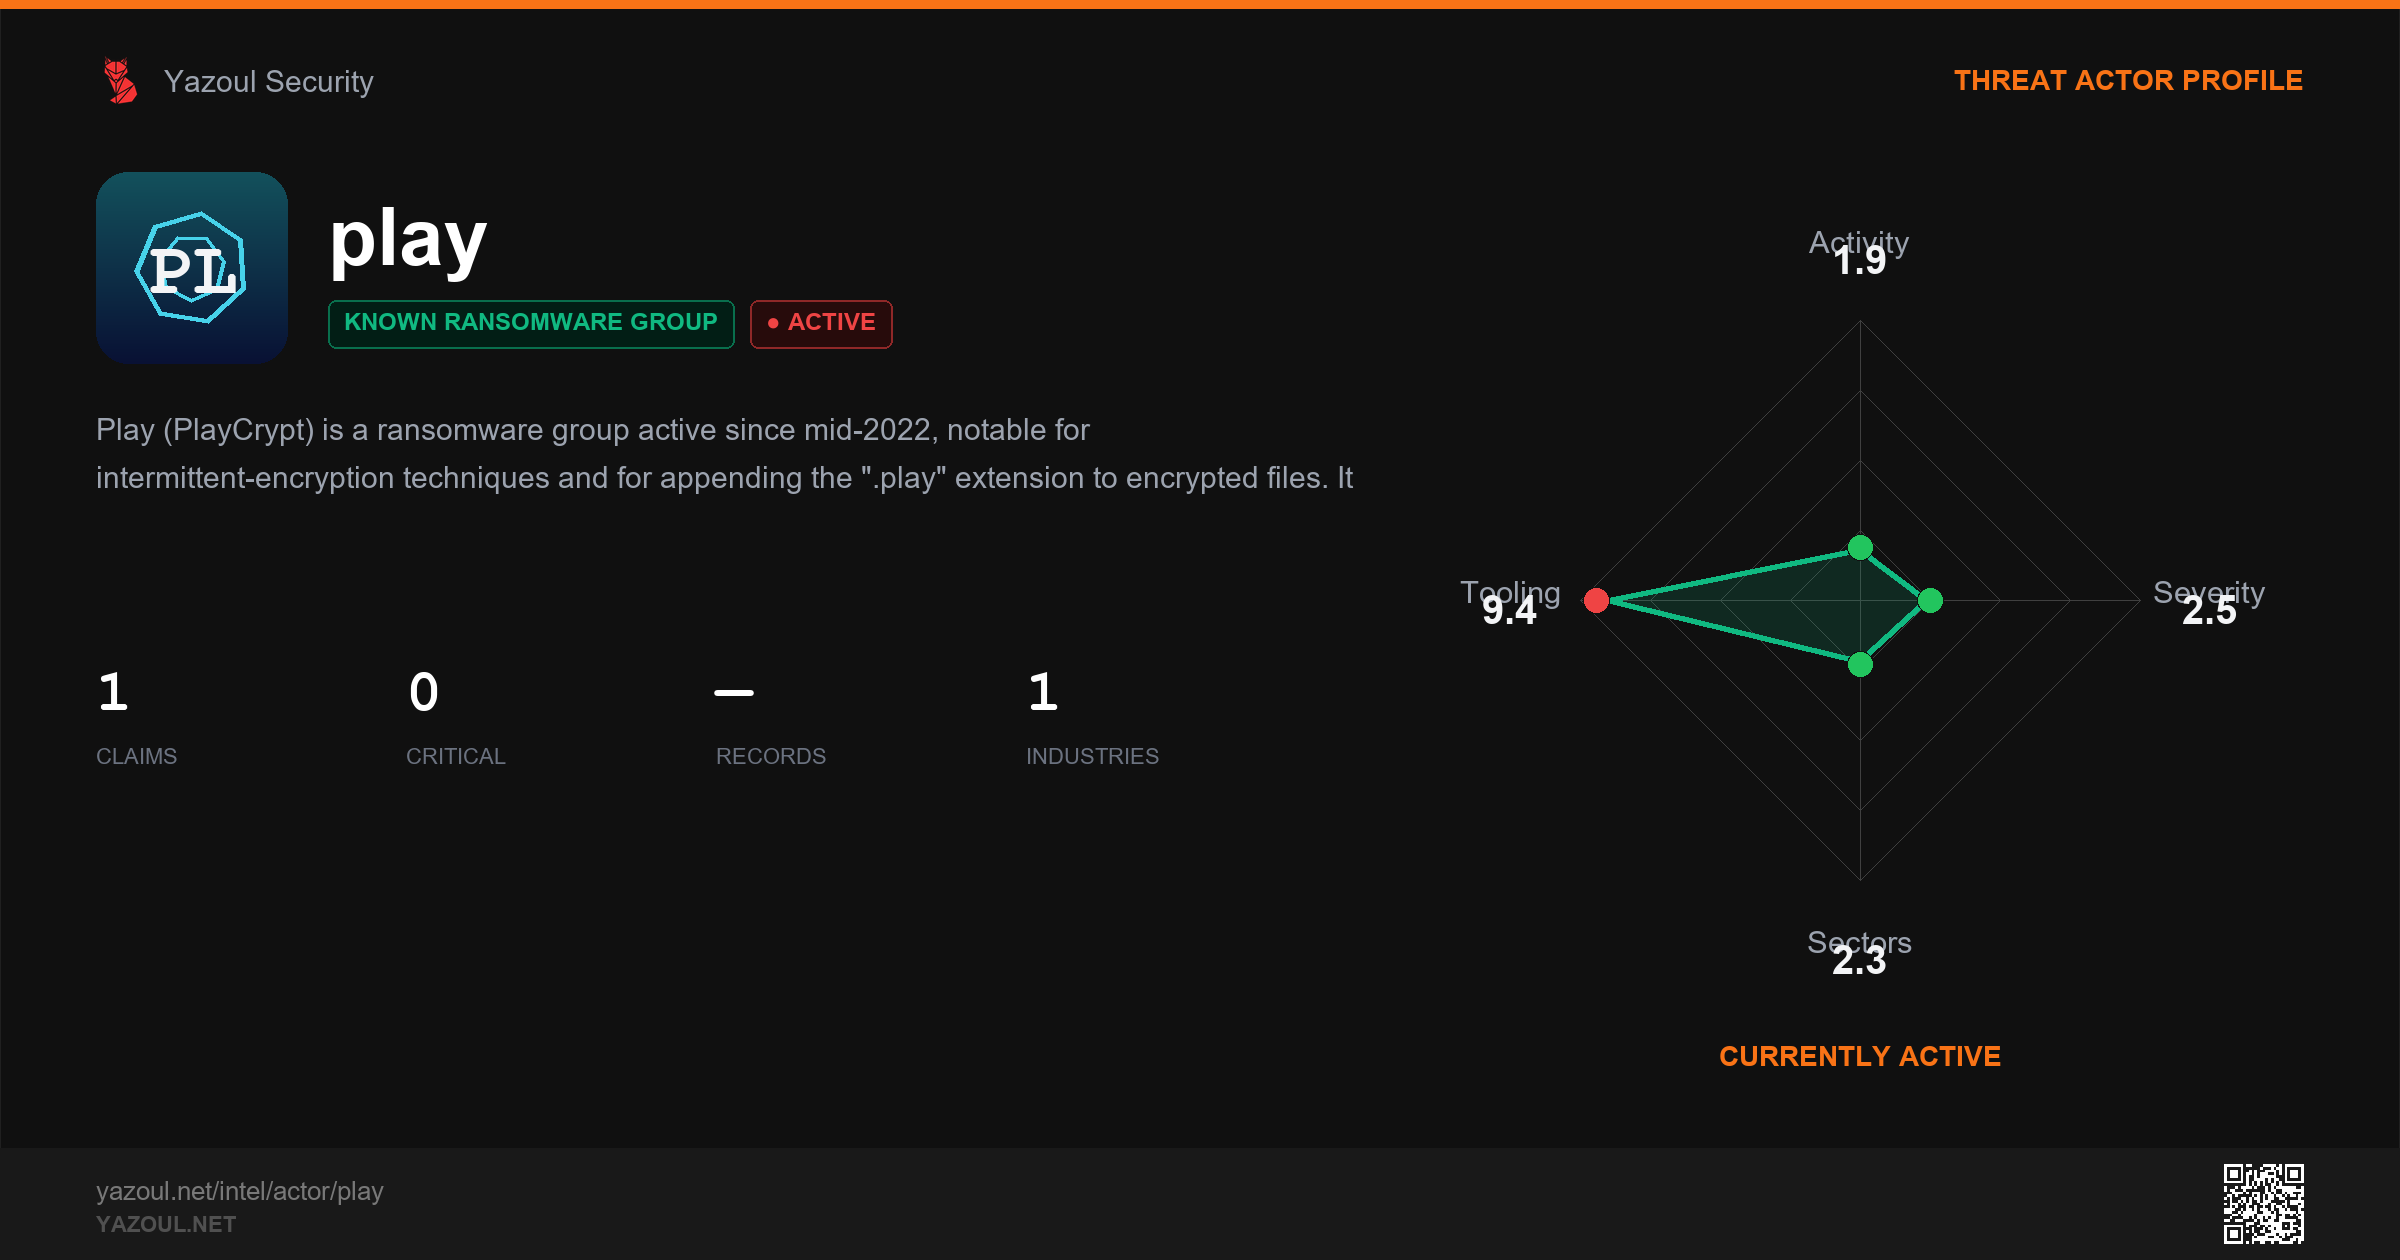
Play (PlayCrypt) is a ransomware group active since mid-2022, notable for intermittent-encryption techniques and for appending the ".play" extension to encrypted files. It has hit government, IT, and critical-infrastructure targets worldwide and runs a double-extortion leak site.
4
Total Claims
2
Critical
—
Records Claimed
3
Industries Hit
Active span: Jun 6, 2026 – Oct 27, 2026 · 4 organizations targeted
Currently active
Actor Threat Profile
Activity Timeline
Peak: Oct 2026 (3)Jun 2026
LessMore
Oct 2026Share this profile
Top Targeted Industries
Financial Services 2
Transportation 1
Transportation/Logistics 1
Tradecraft & Infrastructure
0
Documented tools
15 / 54
MITRE tactics / techniques
4
Known leak sites
Targeted Organizations
Claims by play
Low
Ransomware Claim: Tailormade Logistics
Tailormade Logistics
play
Ransomware Transportation
Oct 28, 2026 Critical
Ransomware Claim: Pure Options
Pure Options
play
Ransomware Financial Services
Oct 17, 2026 Critical
Ransomware Claim: WSBI-ESBG
WSBI-ESBG
play
Ransomware Financial Services
Oct 17, 2026 Low
Ransomware Claim: Pearson Ford
Pearson Ford
play
Ransomware Transportation/Logistics
Jun 7, 2026