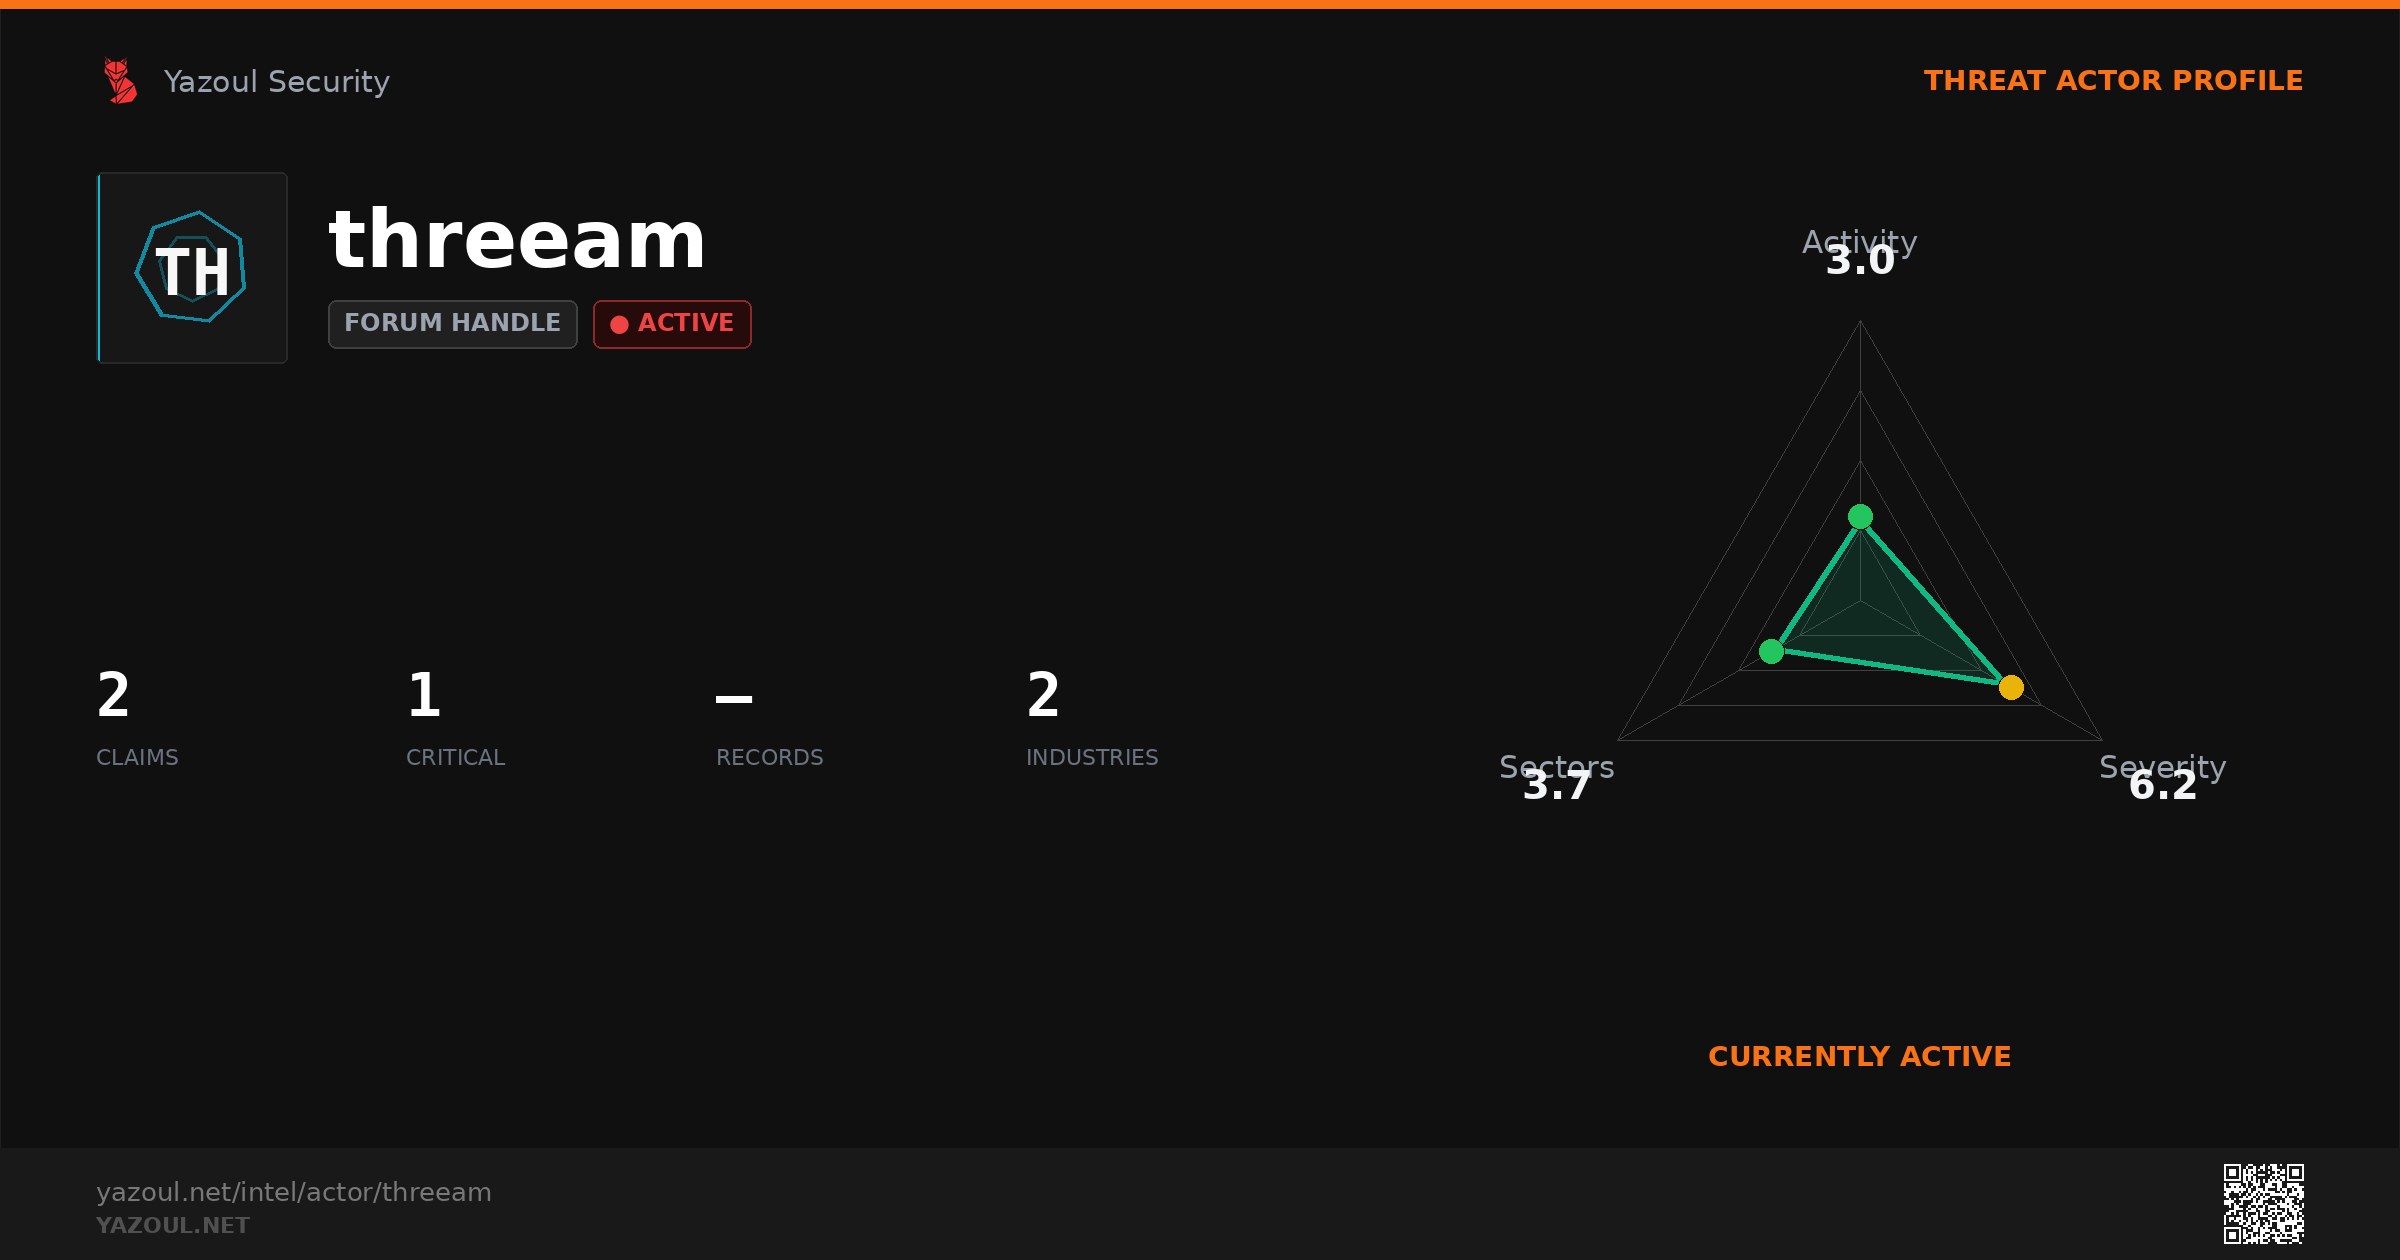
threeam
Known ransomware group ACTIVEA new Ransomware family identified by the name '3AM' or 'ThreeAM' in September 2023. The ransomware operation was observed by the Symantec team, in which a ransomware affiliate attempted to deploy another ransomware, LockBit, on the target network and then switched to 3AM when LockBit was reportedly blocked.<BR> > <BR> > The ransomware operation, according to the publication on its Tor-based website, has been operating since mid-August 2023, according to the publication from its first victim.<BR>Source: https://github.com/crocodyli/ThreatActors-TTPs
2
Total Claims
1
Critical
—
Records Claimed
2
Industries Hit
Active span: Sep 28, 2026 – Sep 28, 2026 · 2 organizations targeted
Actor Threat Profile
Activity Timeline
Peak: Sep 2026 (2)Share this profile
Top Targeted Industries
Tradecraft & Infrastructure
0
Documented tools
6 / 11
MITRE tactics / techniques
2
Known leak sites