AuditTeam
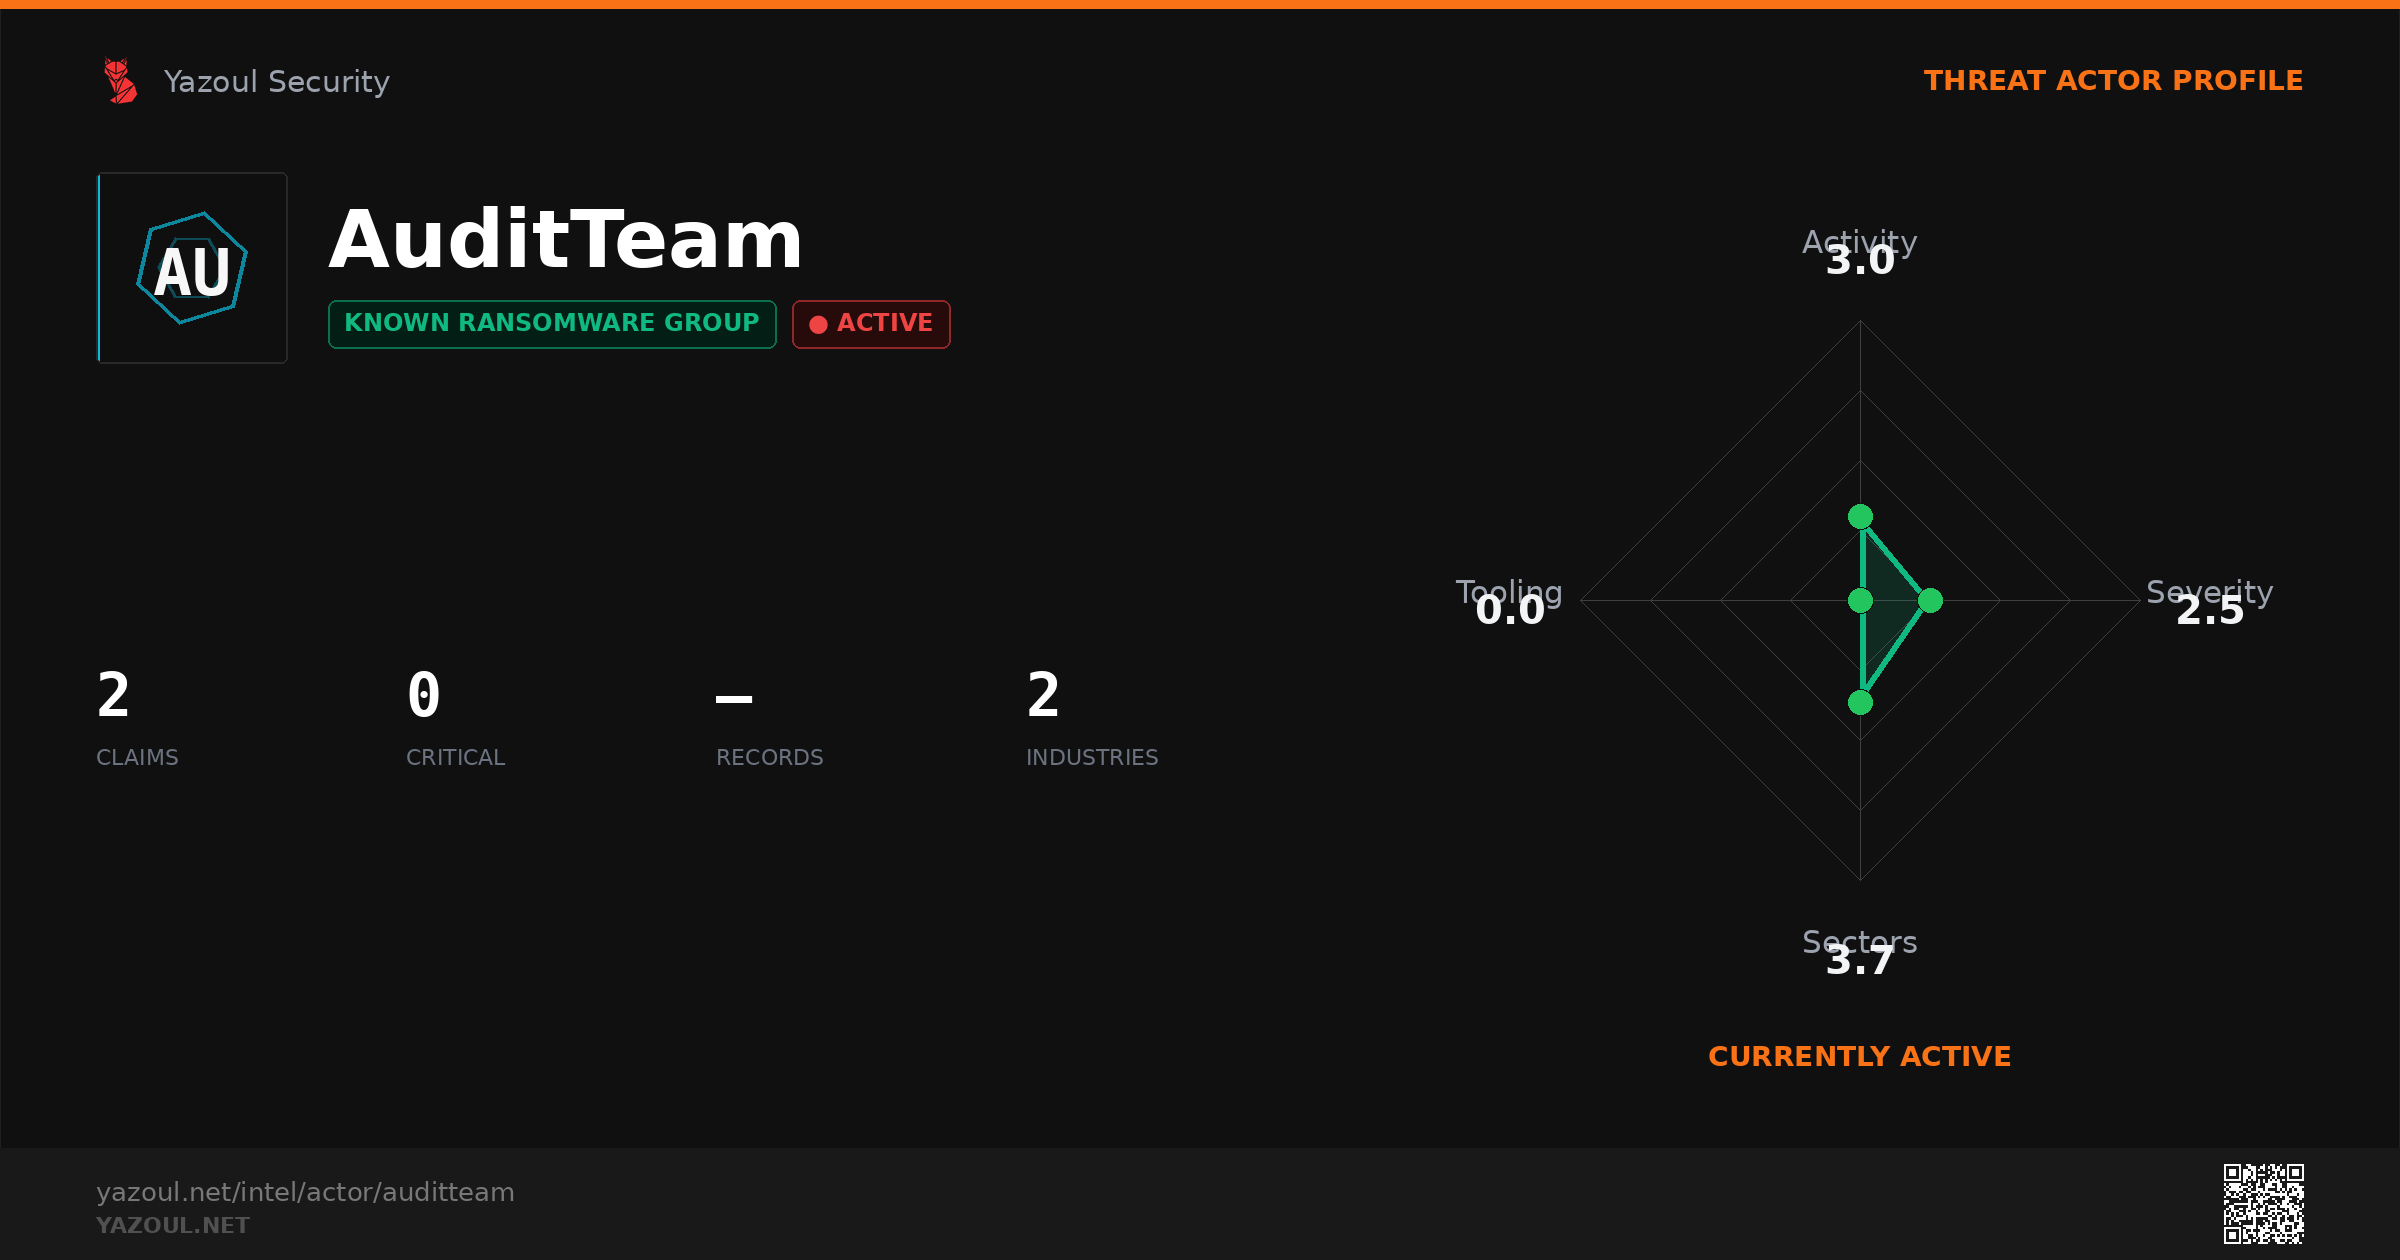
Known ransomware group ACTIVE Currently active
AuditTeam is a small ransomware group with approximately 5 known victims, primarily targeting organizations in East and Southeast Asia across technology and manufacturing sectors, operating a data leak site consistent with double-extortion methodology.
2
Total Claims
0
Critical
—
Records Claimed
2
Industries Hit
Active span: Sep 8, 2026 – Sep 13, 2026 · 2 organizations targeted
Currently active
Actor Threat Profile
Activity Timeline
Peak: Sep 2026 (2)Sep 2026
LessMore
Sep 2026Share this profile
Top Targeted Industries
Education 1
Transportation 1
Tradecraft & Infrastructure
0
Documented tools
0 / 0
MITRE tactics / techniques
2
Known leak sites