osiris
Known ransomware group ACTIVE Currently active
Osiris is a ransomware-as-a-service operation first observed in November 2025 that uses a Bring Your Own Vulnerable Driver (BYOVD) technique to disable endpoint detection tools before deploying hybrid ECC + AES-128-CTR encryption; Symantec researchers linked its operators to former INC ransomware affiliates.
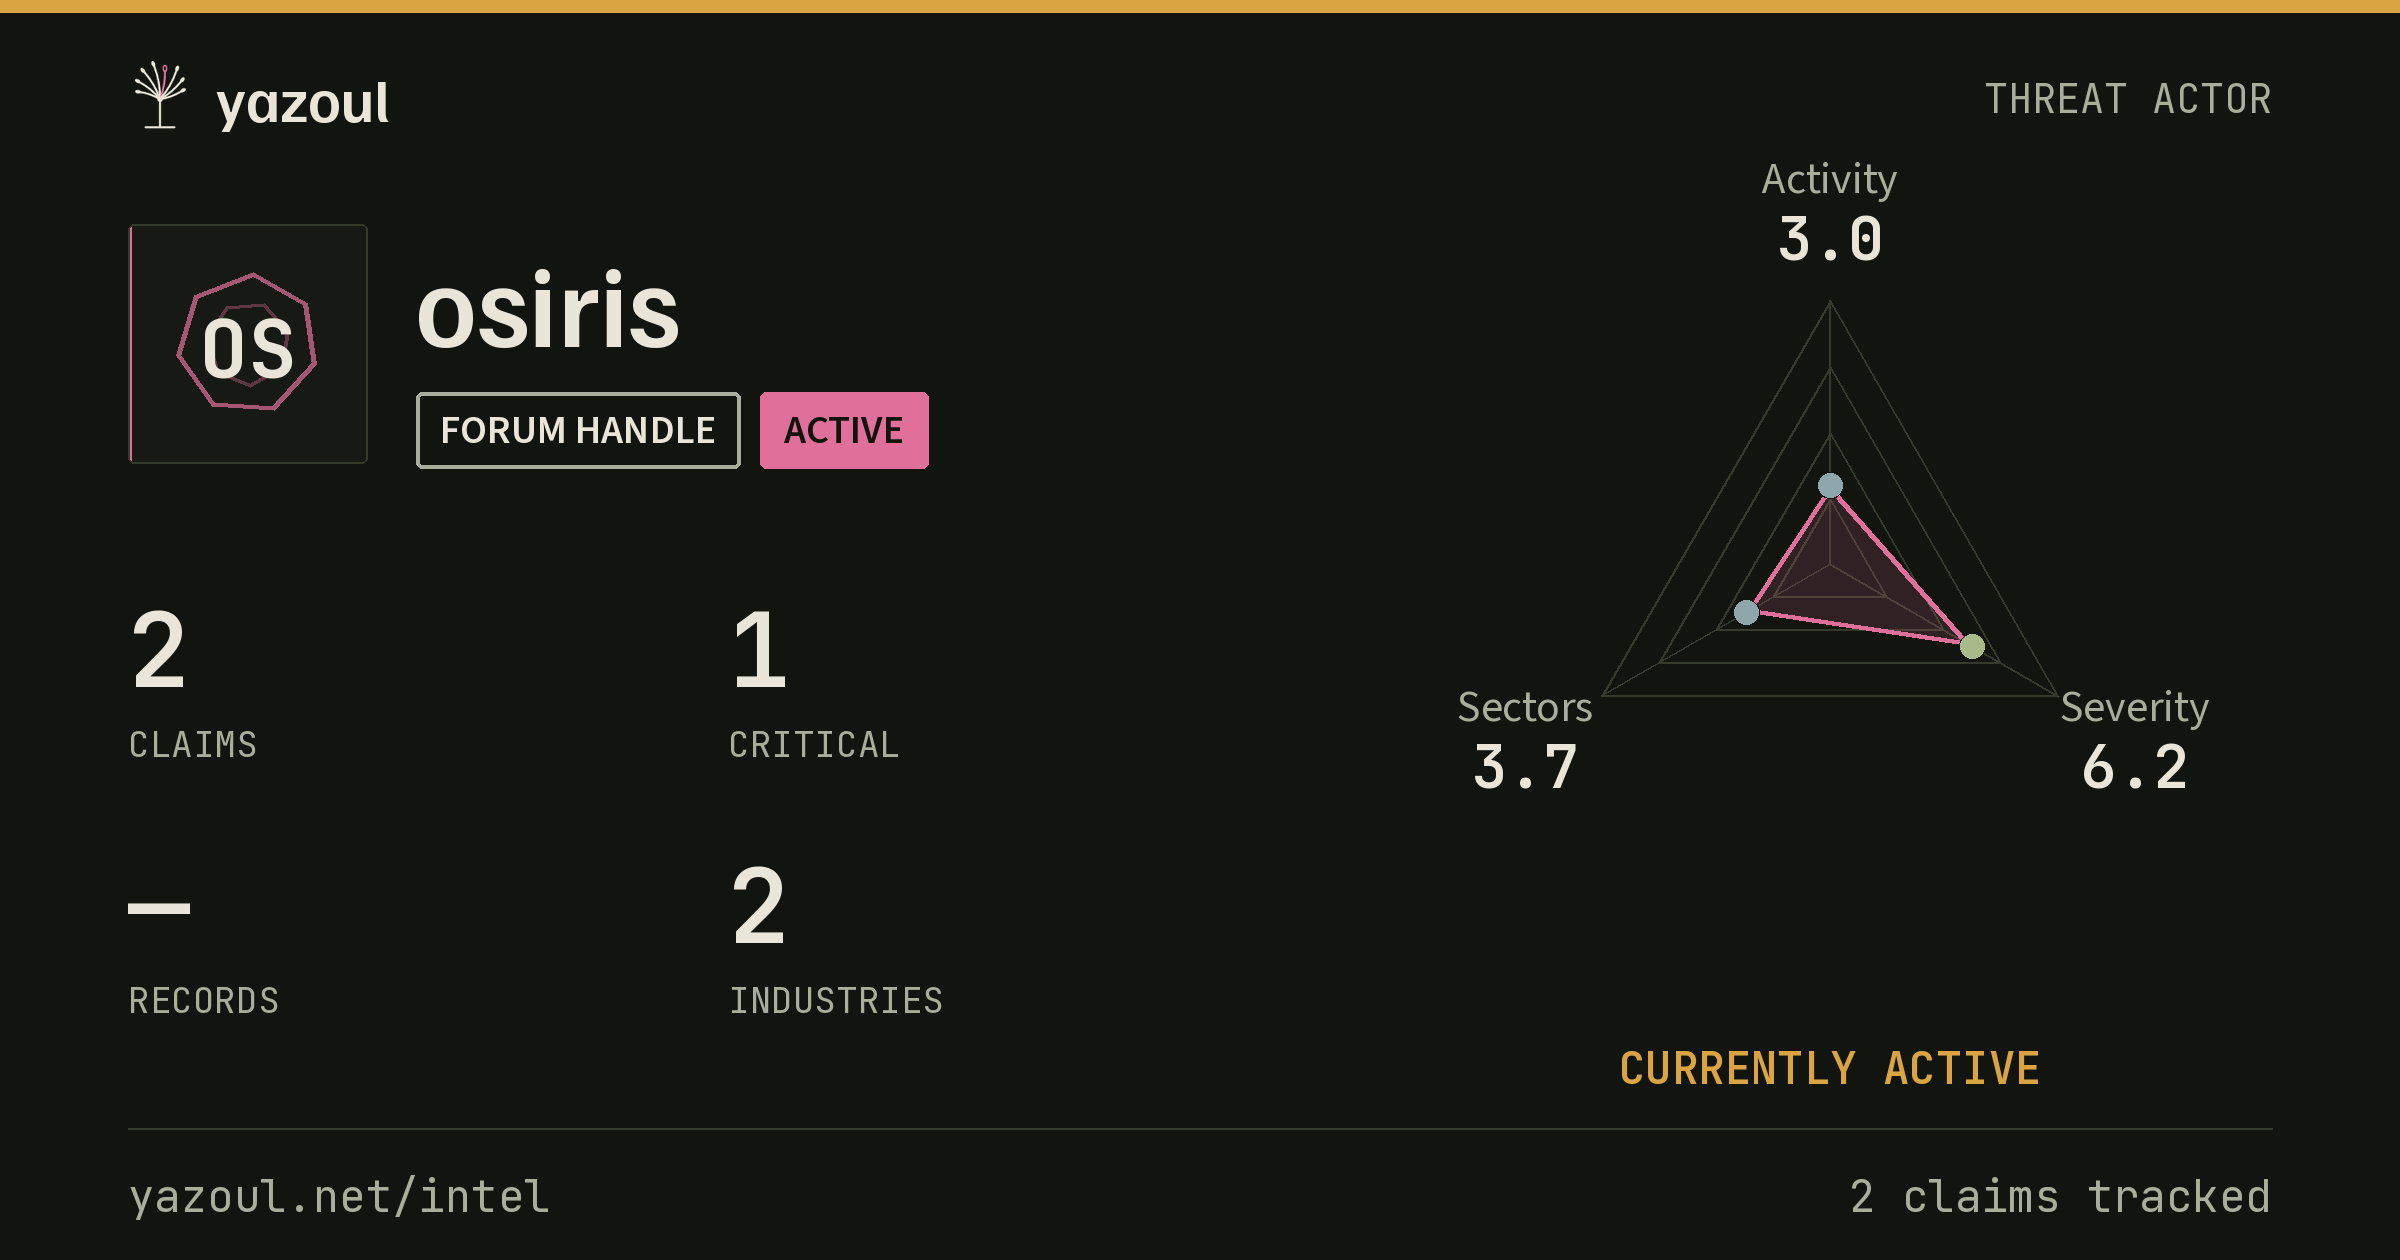
2
Total Claims
1
Critical
—
Records Claimed
2
Industries Hit
Active span: Oct 27, 2026 – Nov 6, 2026 · 2 organizations targeted
Currently active
Actor Threat Profile
Activity Timeline
Peak: Oct 2026 (1)Oct 2026
LessMore
Nov 2026Share this profile
Top Targeted Industries
Healthcare 1
Transportation 1
Tradecraft & Infrastructure
0
Documented tools
0 / 0
MITRE tactics / techniques
2
Known leak sites